How to Spot a Phishing Email in 2026 (They’ve Got Better)
How to spot a phishing email in 2026: AI has fixed the typos, so judge the request instead. The warning signs that still work, plus…

Quick answer: Patch Tuesday is the second Tuesday of every month, when Microsoft releases its security updates. October 2026 set a record, with more than 1,400 flaws fixed in a single release, including one already being used by attackers. For a small business, the job is simple to describe: get the exploited and critical fixes onto every device within days, test the rest, and prove it happened.
Most business owners never think about Patch Tuesday. Their laptops restart one evening, a few updates install and life carries on. That quiet routine has just become a lot less quiet.
On 13 October 2026, Microsoft released fixes for 1,413 security vulnerabilities in one go, according to the Splashtop breakdown of the release. The previous monthly record, set only in September, was 974. Searchlight Cyber points out that October alone beat the roughly 1,100 fixes Microsoft shipped across the whole of 2025.
This guide explains what Patch Tuesday is, why the numbers have jumped, what it means for an Aberdeen business with 10 to 100 staff, and how to keep on top of it without losing a week to updates.
Patch Tuesday is Microsoft’s monthly security release. On the second Tuesday of each month, Microsoft publishes updates for Windows, Microsoft 365 and Office apps, Exchange, SharePoint, SQL Server, Azure services and more. Each fix closes a known weakness, usually listed with a CVE number so security teams can track it.
The predictable schedule exists for a reason. IT teams can plan testing and rollout around a known date, rather than reacting to random releases. The full list for each month sits in the Microsoft Security Update Guide, which is the primary source we check every month.
Emergency fixes can still appear outside the cycle when something is being actively attacked. For planning purposes, though, the next scheduled release is Tuesday 10 November 2026.
The jump from 974 to more than 1,400 fixes is not a sign that Microsoft’s software suddenly got worse. Searchlight Cyber reports that the surge is linked to Microsoft using AI to hunt for flaws in its own products, and that the company had warned this would bring a flood of patches.
In other words, the tools that find problems have become much faster. The people who install the fixes have not. That gap is the real story for business owners.
The release covered almost everything a typical office runs. Windows, Office apps, Outlook, Exchange Server, SharePoint and developer tools were all included. Elevation of privilege and remote code execution flaws made up roughly 70 percent of the total. Those are the two types attackers like most: one gets them in, the other gives them control.
Out of 1,400 fixes, a small handful deserve your attention first.
One vulnerability, CVE-2026-96951, was already being used by attackers when the fix came out. It is a security feature bypass in Windows Shell. Searchlight Cyber notes it can be triggered by a crafted file delivered through phishing, messaging or a malicious website. Microsoft rated it Important rather than Critical, which is exactly why severity labels alone are not enough.
Searchlight Cyber also highlights CVE-2026-70242, an Outlook Reading Pane flaw rated 9.8 out of 10. It needs no click and no login. Previewing a malicious email could be enough. If your team lives in Outlook all day, and most do, this fix should not wait for a quiet week.
Both link back to a theme we see constantly: email is still the front door. Our guide on how to spot a phishing email in 2026 covers the human side of that problem.
You don’t need to read 1,400 CVE entries. You do need confidence that three things are true.
The risk is not theoretical. Unpatched software remains one of the most common ways attackers get into small businesses. Once a fix is public, attackers can study it to work out exactly what was broken, so the clock starts ticking on release day.
Remote and hybrid staff make this harder. A laptop that rarely connects to the office network can drift months behind. We covered this in more detail in why remote workers are your biggest IT security risk.
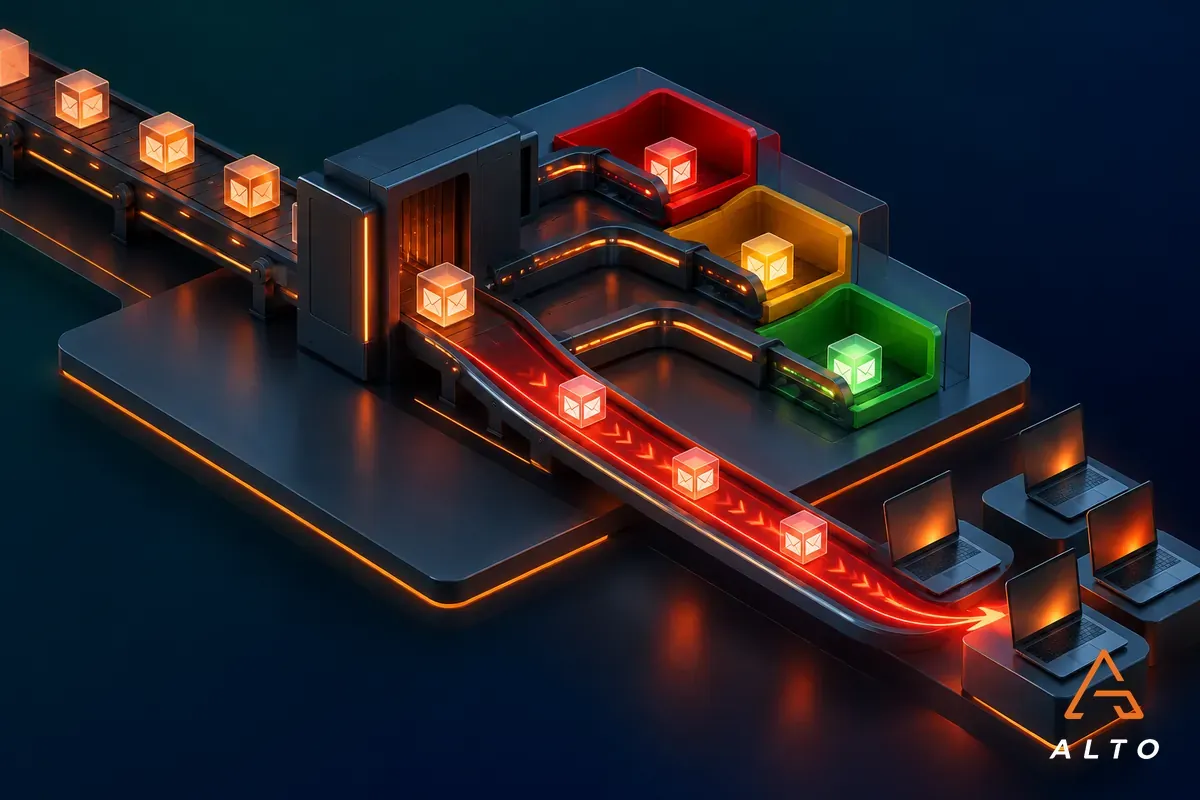
A simple way to handle a big release is to sort it into three groups.
The point is not to treat every patch as an emergency. With 1,400 of them, that would be impossible. The point is to make sure the dangerous few never sit in the “later” pile.
If you hold Cyber Essentials, or plan to, patching is not optional. The scheme requires high-risk and critical security updates to be installed within 14 days of release on all in-scope devices. Unsupported software that no longer receives updates has to be removed or isolated.
A record month makes that 14-day window harder to hit by hand. It also makes it easier to fail an assessment without realising. Our article on Cyber Essentials in 2026 explains what assessors now look for.
Insurers are asking similar questions. Many renewal forms now ask how quickly critical updates are applied, and a vague answer can affect cover. See our guide to cyber insurance requirements in 2026 for the questions to expect.
Good patching is boring, and that is the goal. In practice, it usually includes:
Patching is one part of a wider proactive approach. As we’ve written before, proactive IT support means more than just patch management, but without it, the rest is built on sand.
Even well-run businesses occasionally miss a device or a fix. If you suspect an unpatched system has been exploited, isolate it from the network, call your IT provider and avoid wiping anything until it has been looked at.
Having a plan before you need it makes a large difference. Our guide to what happens after a cyber attack walks through the first 72 hours step by step.
AI-assisted flaw hunting is not going away. If anything, monthly releases are likely to stay large. That is good news in the long run, because flaws found by Microsoft are flaws closed before criminals find them. In the short run, it puts more pressure on small teams who already juggle IT alongside their day jobs.
For many North East firms, the practical answer is to stop treating patching as a background chore. Give it an owner, a deadline and a report. Whether that owner is someone in-house or a managed provider, the question to ask each month is the same: are we fully patched, and how do we know?
The next scheduled Microsoft release is Tuesday 10 November 2026. Patch Tuesday falls on the second Tuesday of every month, with emergency fixes released in between when needed.
You should install all updates that apply to your systems, but not all at the same speed. Exploited and critical fixes come first, within days. Lower-risk fixes can follow after a short test.
Searchlight Cyber reports the surge is linked to Microsoft using AI tools to find flaws in its own software. More flaws are being found faster, which means larger monthly releases.
It helps, but it is rarely enough on its own. Automatic updates can stall, get postponed by users or miss third-party software. You also get no evidence for Cyber Essentials or your insurer without central reporting.
Cyber Essentials requires high-risk and critical security updates to be applied within 14 days of release on all in-scope devices.
If you can’t say with confidence that every device in your business has October’s fixes installed, it’s worth finding out before 10 November adds the next batch. Alto offers a free patching and security health check for Aberdeen and North East businesses. We’ll show you which devices are behind, what needs fixing first and how to keep it that way. Get in touch with our cyber security team to book yours.